Your farm data stays yours
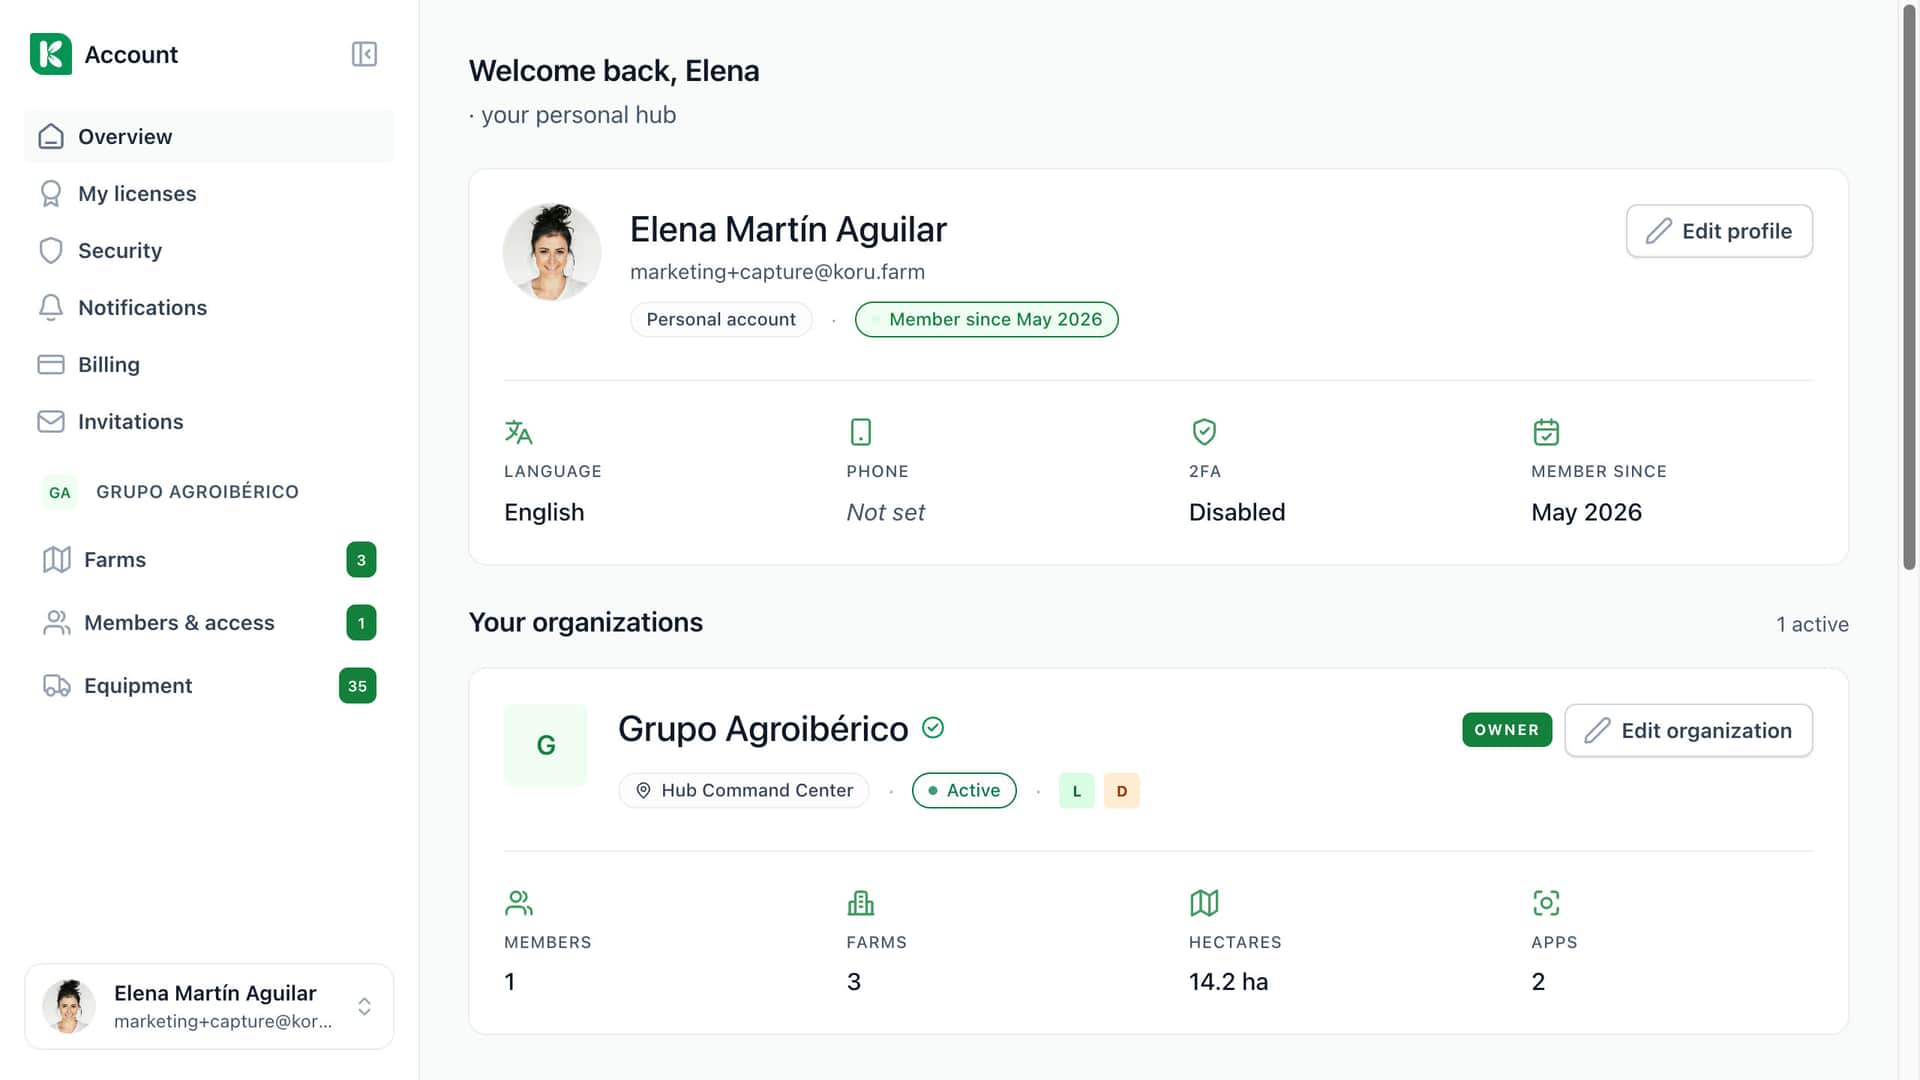
Koru was designed under GDPR from day one. Your farm data — parcels, activities, workers, products — is stored on EU infrastructure, encrypted at rest and in transit, and never shared with third parties without explicit consent. Sign-ins and actions on your farm are written to an audit log, and each member sees only what their role allows.
On the screen
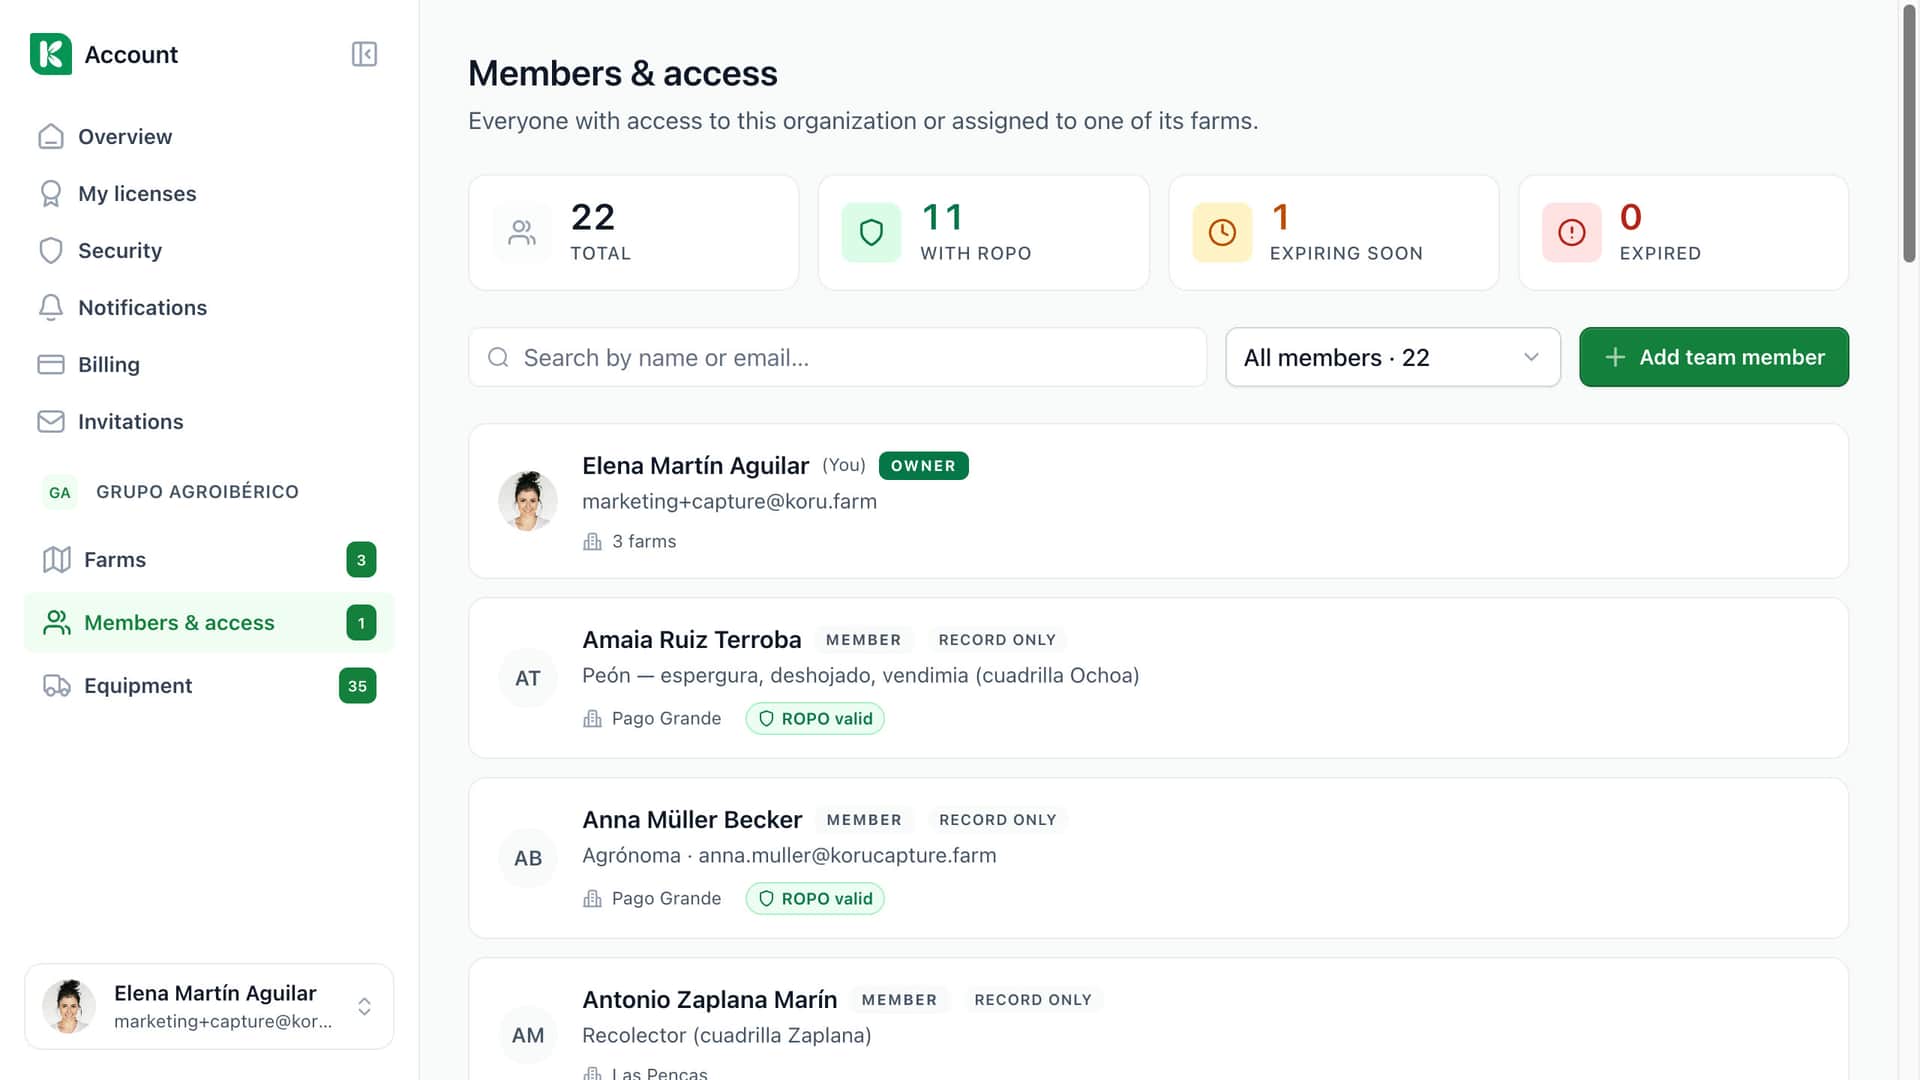
Who has access, and to what
Everyone with access to the organisation or assigned to one of its farms.
ROPO at a glance
22 people, 11 with ROPO, 1 expiring soon, none expired.
Owner, member, record only
Each person has a role: owner, member, or only on record.
Which farms
The farms each person is assigned to — Elena to 3, others to Pago Grande.
ROPO valid
A valid ROPO card is marked on the person.
Stored in the EU. AI, stated plainly.
Your farm records live in a database in Ireland, and the Koru app runs in Dublin. Backups stay in the EU. One exception, stated plainly: when you use the AI assistant, the request goes to AI providers outside the EU — Anthropic, OpenAI and Google — and they receive only what the answer needs.
- All production data hosted on EU infrastructure
- Backups stored exclusively within the EU
- AI providers outside the EU receive only what each answer needs
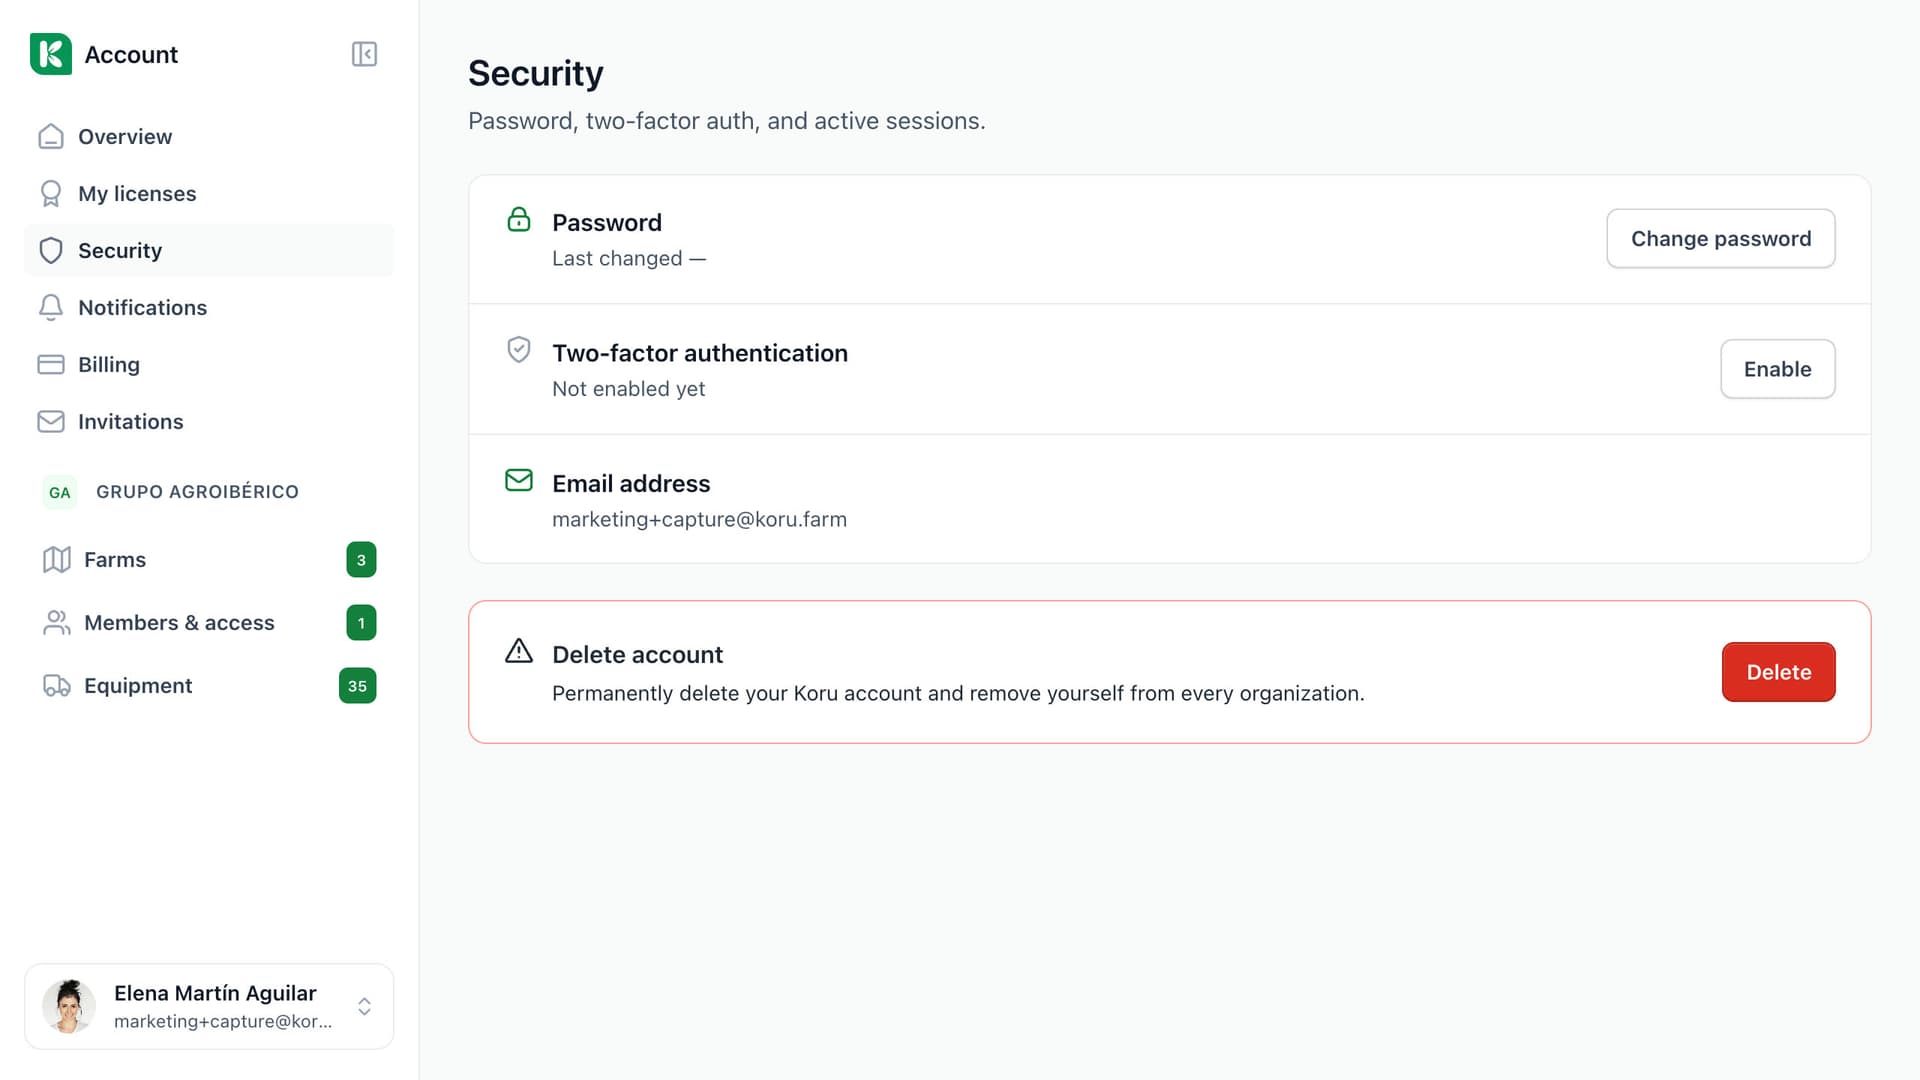
Two-factor sign-in and a log you can read.
Turn on two-factor sign-in and Koru asks for the second factor every time you sign in. Sign-ins are recorded. The audit log groups actions by day, names who acted and on what, and filters by person and type. Koru staff can enter a farm only through a recorded impersonation session, which cannot erase data.
- Two-factor sign-in, asked at every sign-in once enabled
- Audit log by day, filtered by person and type
- Koru staff access only through recorded impersonation
Security and privacy, built into every layer.
The guarantees you need when your data is your livelihood.
EU data residency
Your records, the app and its backups are hosted in the EU. The one exception — AI requests — is named on this page.
Encryption everywhere
Data encrypted at rest with modern ciphers, and in transit with TLS 1.3.
Readable audit log
Actions on your farm grouped by day, with who acted and on what. Filter by person and type.
Two-factor sign-in
Enable a second factor and Koru asks for it at every sign-in. Sign-ins are recorded in the audit log.
Role-based access
Granular permissions so workers, advisors, and owners each see only what they should.
Only what the answer needs
When you ask the assistant, the AI provider receives the records needed to answer — not your whole farm.
AI providers, named
Anthropic, OpenAI and Google process AI requests outside the EU. We name them here instead of hiding them in a clause.
Recorded staff access
Koru staff can enter a farm only through a recorded impersonation session, and that session cannot erase data.
For anyone who takes 'it's just farm data' seriously.
Single farm
You get EU residency, two-factor sign-in, and an audit log of actions on your farm — without reading a white paper.
Advisor
Advisors can demonstrate compliance posture to every client with EU residency, encryption, and audit logging built in.
Cooperative
Cooperatives get documented EU residency, role-based access, and audit logs — the things a board needs to sign off on supplier risk.